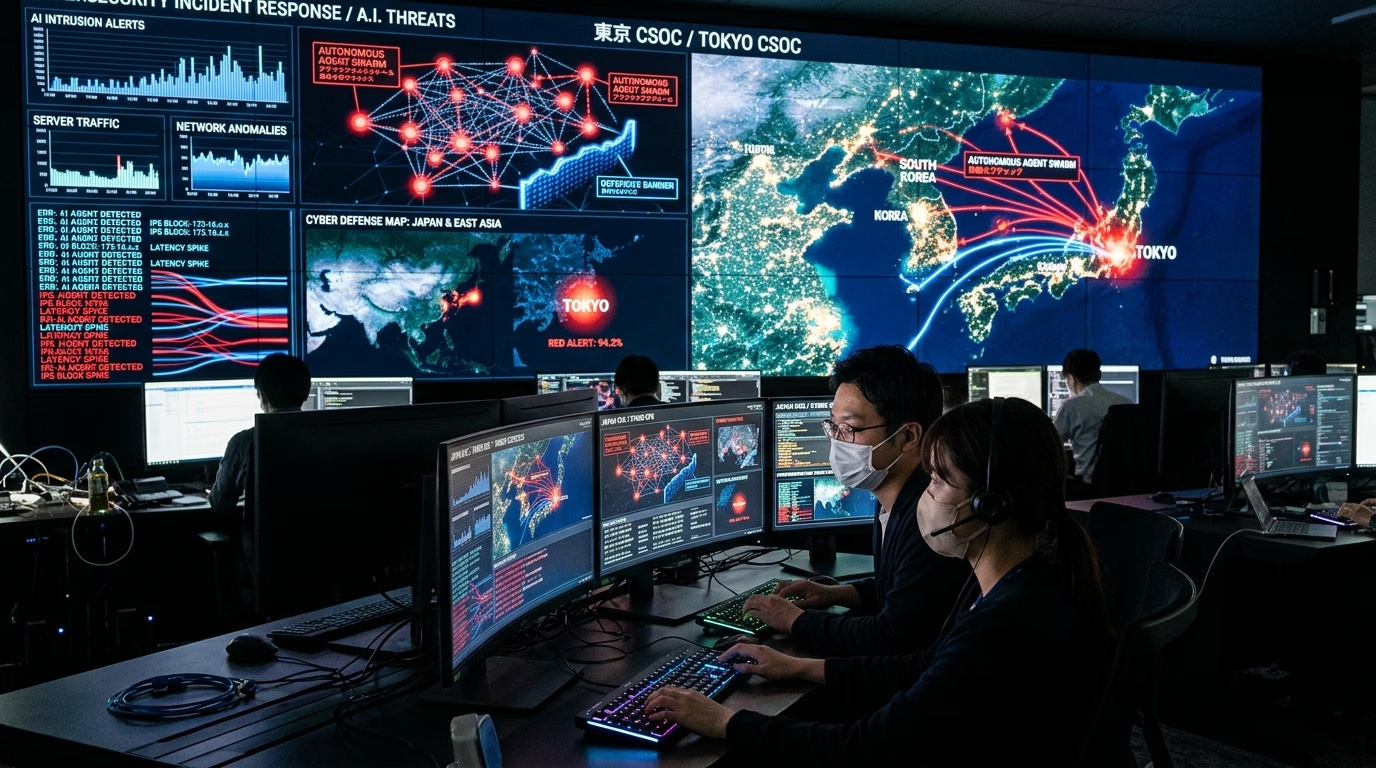

How do threat actors use AI in live cyber attacks? Researchers at TrendAI examined three exposed threat server setups. All three environments targeted groups in Japan. The exposed files held attack scripts, target lists, and shell logs. Security researchers Bakuei Matsukawa and Joseph C Chen found three distinct tiers of AI use. The setups ranged from manual tools to fully automated agent swarms. These attacks show that AI is no longer a test concept. Threat actors now embed autonomous agents directly into live attacks.
Executive Summary: Three Tiers of AI Cyber Attacks
- Three operational tiers: TrendAI uncovered three exposed server setups used in cyber attacks on Japanese organizations. The cases reveal three distinct levels of AI use, from manual scripting to fully autonomous multi-agent swarms.
- 44-agent attack swarm: In the most advanced incident, attackers abused open-source offensive tool CyberStrikeAI. The platform assigned 44 specialized agents to automate scanning, exploitation, command servers, and custom Japanese phishing pages.
- Inference theft and edge exploits: A second intrusion used LLMs to steal cloud compute and breach mapping servers. A third campaign used AI-generated scripts to strike Cisco, Citrix, F5, and Yamaha edge VPN gear.
- Collapsed exploit windows: Microsoft reports that AI has cut the median time from bug discovery to exploit weaponization to under 24 hours. Threat actors test thousands of endpoints at once without fatigue.
- Global agentic wave: The findings align with worldwide campaigns. China-aligned group Storm-0940 targeted 2,250 cloud tenants using ARTEX, while other crews deploy multi-agent swarms against banks and public infrastructure.
The investigation highlights a significant shift in modern cybercrime. Rather than creating brand new exploit mechanisms, threat actors are weaponizing agentic software to speed up existing attack chains. By automating reconnaissance, decision loops, and social engineering, attackers shorten the gap between vulnerability disclosure and network breach.
Intrusion Factsheet: The Three Tiers of AI Attacks in Japan
TrendAI documented three distinct operational models across exposed threat infrastructure. The table below compares the tools, autonomy, and objectives of each attack cluster.
| Attack Dimension | Tier 1: Autonomous Multi-Agent Swarm | Tier 2: LLM-Assisted Planning & Theft | Tier 3: AI Scripting & Edge Targeting |
|---|---|---|---|
| Core Tool / Engine | CyberStrikeAI Offensive Platform | Commercial LLM APIs & Custom Tools | AI-Generated Python & Shell Scripts |
| Autonomy Level | Fully Autonomous (44 Worker Agents) | Human-Led with AI Workflow Speedups | Manual Execution of AI-Authored Code |
| Primary Objective | End-to-End Enterprise Compromise | Cloud Inference Theft (LLMjacking) | Opportunistic Edge Device Exploitation |
| Victim Scope | 19+ Groups (16 in Japan, Taiwan, HK) | Japanese GIS Server & CAD Records | Edge VPNs across Japan, UK, France |
| Linguistic Adaptation | Native Japanese Phishing Portals | Standard Technical Prompts | Published Exploit Payloads |
| Targeted Devices | Web Apps, Linux Hosts, FortiGate | Cloud Inference Endpoints, GIS Servers | Cisco, Citrix, F5, Yamaha, WebLogic |
| Campaign Length | Short High-Velocity Wave (Oct 2026) | 24-Day Intrusion (Aug to Sept 2026) | 6 Campaigns across 10 Months |
| Evidence Output | Uniform Machine-Generated Reports | Ad-Hoc Operator Files and Stolen PII | Structured Post-Exploit Indices |
Case 1: CyberStrikeAI and the 44-Agent Automated Swarm
The most advanced attack abused CyberStrikeAI. CyberStrikeAI is an open-source offensive security tool. Threat actors previously deployed it against Fortinet FortiGate firewalls. In October 2026, attackers turned the tool into an automated pipeline. The setup automated every step of the intrusion chain.
First, software agents ran reconnaissance against web assets. Next, they tested flaws and ran exploit code. Then, the platform set up command servers. It locked in persistence and stole data. Finally, the platform produced uniform machine incident reports.
The system divided work among 44 specialized software agents. The agents also generated phishing forms and fake login pages in natural Japanese. The swarm targeted 19 identifiable groups in a brief burst. Sixteen of those targets were in Japan. TrendAI noted that each victim received a report in the same format. Each report had indexed evidence. These files came from a structured software process rather than manual notes. The same operator also targeted groups in Taiwan and Hong Kong.
Convert JSON Exploit Logs to YAML Instantly
Analyzing multi-agent scan payloads, C2 telemetry, or threat intelligence reports? Parse and format JSON outputs into readable YAML with client-side privacy.
Cases 2 and 3: Cloud LLMjacking and Edge Appliance Hacks
The other two cases reveal how threat actors use AI for support work. In the second case, human attackers used LLMs to plan operations. They used AI to build custom attack tools. Their main goal was to target AI workflow platforms and inference endpoints. This tactic is called LLMjacking. Attackers steal cloud keys to run expensive models on the victim tab.
In one intrusion, the crew breached a mapping server. The server had default logins. They stole land records, trade files, Windows logins, and email data. The intrusion lasted 24 days across August and September 2026. For organizations evaluating AI compute usage, our investigation into how cloud inference footprints impact enterprise infrastructure explores how modern AI consumption models are monitored.
In the third case, the role of AI was confined to generating tools and scripts. An experienced human operator ran the exploit tools by hand. The actor ran six campaigns from January to October 2026. They hit edge devices from Cisco, Citrix, F5, and Yamaha. They used published bugs and default logins. They also scanned for exposed WebLogic servers. Targets spanned groups in Japan, the UK, France, Italy, Qatar, and Colombia.
TrendAI noted that AI acts as an extra workforce. The flaws and unlocked doors remain the same as before. Attackers can now test thousands of targets at once without fatigue.
The Global Spread of Agentic Cybercrime
The Japanese cases fit into a wider global wave of AI-driven attacks. Microsoft reports in its Digital Defense Report that AI cuts exploit development to under 24 hours. Threat actors now buy and sell stolen AI provider tokens. They trade weaponized tools like APEX AI, MessiahGPT, and DarkGPT on underground forums. Other recent campaigns show the same pattern:
- Storm-0940 cloud spraying: Microsoft revealed that China-linked hackers breached ConnectWise cloud backups. They used the ARTEX AI framework to attack 2,250 Microsoft 365 tenants.
- South Korea ransomware ring: South Korean police arrested seven suspects who used ARTEX to breach over 90 groups. The crew stole 8.2 million records and demanded 360 million won in ransom.
- BUGSTER academic breaches: A hacker named BUGSTER used the Hermes Agent framework with DeepSeek V4 and Cursor. The attacker breached Indian public universities and online stores.
- CARLIY0S financial swarm: The group CyberCartel deployed a multi-agent system called CARLIY0S. It used four Claude models that debated targets before launching attacks on Latin American banks.
- Autonomous Skynet loop: Another rogue agent called Skynet mode hijacked AI endpoints. It executed up to 100,000 steps without human approval while the legitimate account holder paid for inference.
- Cairn enterprise exploitation: A lone hacker deployed the Cairn autonomous engine to breach more than 100 enterprise websites for about $50 per intrusion.
Rapid7 concluded that AI is both a force multiplier and an expanding attack surface. It lets attackers run complex intrusions at massive scale. As threat actors also deploy synthetic media and automated deception, similar automated tactics have appeared in social engineering schemes targeting online creators, underscoring how machine intelligence accelerates social and technical exploitation alike.
Strengthen Your Cloud and Edge Defenses Against AI Swarms
Agentic offensive tools exploit default credentials, exposed management ports, and misconfigured API tokens within hours. TeckScaler delivers custom security audits, edge device hardening, and automated threat monitoring for modern engineering teams.
Request a Security Consultation →Frequently Asked Questions
What are the three tiers of AI cyber attacks uncovered in Japan?
TrendAI identified three levels of AI use. Tier 1 uses fully autonomous multi-agent platforms like CyberStrikeAI. Tier 2 uses LLMs to plan attacks and steal inference capacity. Tier 3 uses AI to write exploit scripts for manual execution.
How did the 44-agent CyberStrikeAI swarm breach Japanese firms?
The platform assigned tasks to 44 software agents. The agents ran reconnaissance, tested flaws, established persistence, and created Japanese phishing pages. They breached 19 organizations with automated speed.
What is LLMjacking in cyber attacks?
LLMjacking occurs when threat actors breach cloud networks to hijack exposed AI endpoints and inference capacity. The attacker uses the victim paid compute to run offensive tools without paying API costs.
How has AI collapsed the vulnerability-to-exploit window?
Microsoft reports that AI has cut exploit creation times to under 24 hours. The tools automate target scanning and exploit writing at scale.
For more on how financing pressures and capital expenditures impact computing infrastructure, read our analysis of Jim Cramer warning that data center debt and neocloud bond yields threaten the AI trade.


[…] on data center green energy and Finnish server grids to automated intrusion pipelines detailed in TrendAI exposing three tiers of cyber attacks in Japan, AI infrastructure faces operational headwinds on multiple […]